Tag: AI governance

  • AI Agent Enterprise Data Security and Compliance: A Complete 2026 Guide

    AI Agent Enterprise Data Security and Compliance: A Complete 2026 Guide

    AI agent enterprise data security compliance is the set of controls that keep an autonomous AI agent from leaking data, taking unauthorized actions, or breaking regulations while it works inside your business. It is different from ordinary software security because an agent does not just read data, it acts: it has permissions, calls tools, and makes decisions.

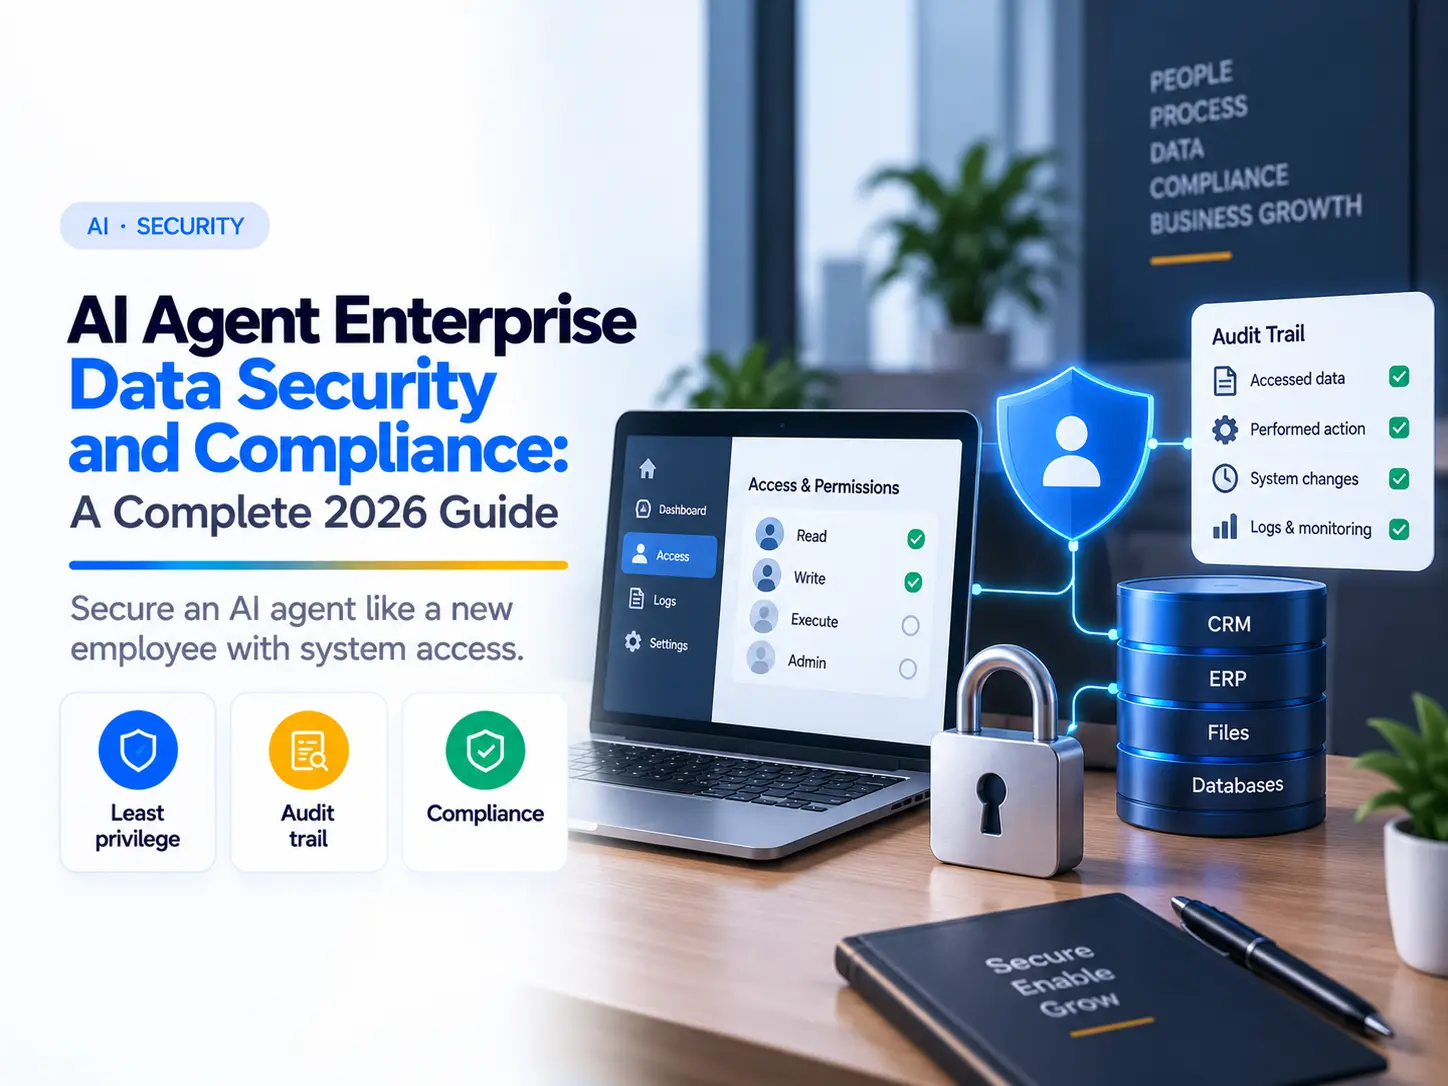
    The essentials are least-privilege access, full audit logging of every action, human approval for high-risk steps, defense against prompt injection, and mapping the agent to the frameworks that apply to you (GDPR, SOC 2, ISO 27001, and the EU AI Act, whose high-risk rules take effect on 2 August 2026). Treat the agent as a powerful new employee with system access, and secure it like one.

    Getting AI agent enterprise data security compliance right is now the hard part of deploying agents, not building them. The models are capable enough. The blocker in most enterprises is proving that an autonomous system with access to customer data, internal tools, and the ability to act will not leak, break a rule, or do something no one authorized. That is a fair concern, and it has real answers.

    This guide is the practical version for teams actually deploying agents. It covers why agent security is different, what compliance actually involves, the specific risks that matter in 2026, how to handle permissions and audit trails, which regulations apply, how to evaluate a vendor, and a concrete checklist to secure an enterprise agent. We build production AI agents at Mobilions, and security and compliance are where most of the engineering effort goes, so this is a practitioner’s view rather than a policy summary.


    Why AI agent security is different from normal software security

    The instinct is to treat an AI agent like any other software vendor or SaaS tool. That instinct undersells the problem, and the difference is the whole reason this is hard.

    Ordinary software follows fixed rules. It does exactly what it was coded to do, and you secure it by controlling its inputs and its access. An AI agent is different in three ways. It acts, calling tools, sending messages, changing records, not just returning information. It has agency, choosing what to do next based on a goal rather than a script, which means its exact behaviour is not fully predictable in advance. And it is manipulable through language, because the same natural-language interface that makes it useful can be hijacked by carefully crafted text.

    Put those together and an agent is less like a database and more like a new employee who is fast, tireless, literal, and occasionally gullible, and who has been handed system access on day one. You would not give a new hire unlimited access to everything and no oversight. The same logic, applied rigorously, is what agent security is.

    AI agent enterprise data security compliance: what it actually covers

    It helps to define the scope plainly, because the phrase covers several distinct jobs. Strong AI agent enterprise data security compliance rests on a few pillars, and a gap in any one is where incidents come from.
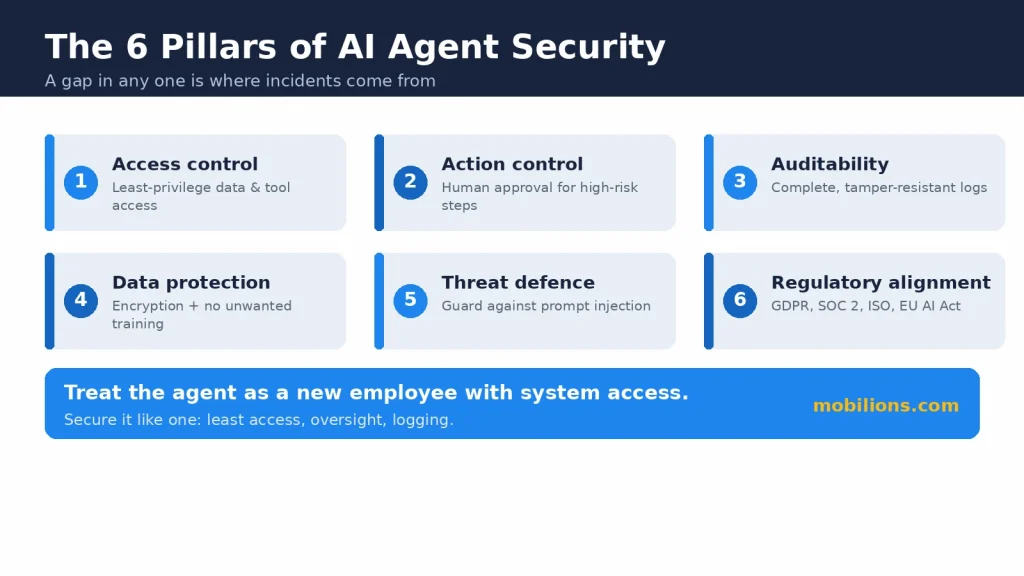
    The six pillars of AI agent enterprise data security compliance: access, action, audit, data, threat, regulatory

    Access control: exactly what data and tools the agent can reach, kept to the minimum it needs. Action control: which operations it can perform on its own, and which require a human to approve. Auditability: a complete, tamper-resistant log of everything the agent did, so you can review, investigate, and prove what happened. Data protection: encryption, control over whether your data trains anyone’s model, and clean deletion when you stop. Threat defence: protection against prompt injection and manipulation. And regulatory alignment: mapping all of the above to the laws and standards that apply to your business.

    Miss access control and the agent can reach too much. Miss auditability and you cannot prove compliance or investigate an incident. Miss threat defence and an attacker turns the agent’s power against you. AI agent enterprise data security compliance is getting all six right together, not picking the easy ones.

    The core risks in 2026

    The threats are not hypothetical any more, so it is worth being specific about what actually goes wrong.

    Prompt injection. This is the big one. An attacker hides instructions in content the agent reads, an email, a web page, a document, and the agent follows them, exfiltrating data or taking actions it should not. OWASP ranks prompt injection as the number one risk for LLM applications, and its 2026 reporting notes there is no complete fix even with frontier models, which is why defence in depth is the only credible strategy. Real, high-severity vulnerabilities in mainstream AI coding and assistant tools through 2025 and 2026 show this is being exploited in production, not just in labs.

    Excessive agency and over-permissioning. An agent given more access or autonomy than it needs is a large blast radius waiting for a trigger. The danger is simple: excessive agency is only a threat if someone can hijack it, and prompt injection is exactly how they do. The fix is least privilege, giving the agent the narrowest access and the fewest autonomous powers that still let it do its job.

    Data leakage. An agent with broad read access can surface sensitive data to the wrong user, include it in an output, or send it somewhere it should not go, often without any malicious attacker involved, just a poorly scoped permission.Enforcing this consistently is the job of a fabric architecture for AI systems, which centralizes access and audit across every model and agent

    Unauthorized actions. Because agents act, an error or a manipulation can turn into a real-world consequence: a wrong record changed, a message sent, a payment attempted. This is why high-risk actions need a human in the loop.

    Unwanted training on your data. If your data flows to a vendor’s model and is used for training, it can effectively leak into a system you do not control. Knowing, and contractually controlling, whether your data trains anyone’s model is a core compliance question.

    Weak oversight. The quiet risk is simply not watching. One 2026 industry survey found only a minority of organizations monitor their AI activity end to end, which means most would not notice a problem until after it caused damage.

    Permissions and access control: the foundation

    If you fix only one thing, fix this, because most agent incidents trace back to an agent that could reach or do too much.

    The governing principle is least privilege: the agent gets the minimum data access and the fewest tool permissions it needs for its specific job, and nothing more. A support agent that answers order questions needs read access to orders, not write access to the finance system. Access should be role-based and scoped, ideally with the agent holding its own identity and permissions rather than borrowing a human’s or a shared admin account, so its actions are attributable and its access is independently controllable.

    A common and important question: should an AI agent have the same access as the employee who runs it? The answer is no. An agent operates faster, at scale, and can be manipulated in ways a person cannot, so it should usually have narrower access than a human doing the same role, with the riskiest capabilities removed entirely or gated behind human approval. Give it employee-level access to everything and you have created an employee who never sleeps, can be tricked with a paragraph of text, and touches your whole system.

    Audit trails and monitoring

    You cannot secure or prove compliance for something you cannot see, so logging is not optional.

    Every meaningful action an agent takes, what it accessed, what it decided, what it did, should be recorded in a complete, time-stamped, tamper-resistant log. Good audit trails do three jobs: they let you investigate when something looks wrong, they let you prove to auditors and regulators what the agent did and did not do, and they let you improve the system by seeing how it actually behaves. Pair the logs with active monitoring and alerting, so unusual behaviour, a spike in data access, an unexpected action, surfaces in near real time rather than in a post-incident review.

    How often should you review? Continuously through automated monitoring, with scheduled human reviews for high-stakes agents. The regulatory direction is the same: the EU AI Act’s high-risk rules require automatic logging and human oversight, so building this in now is also future-proofing.

    Which regulations actually apply

    Compliance is not one rule; it is a stack, and which parts apply depends on your data and industry. The main pieces in 2026:
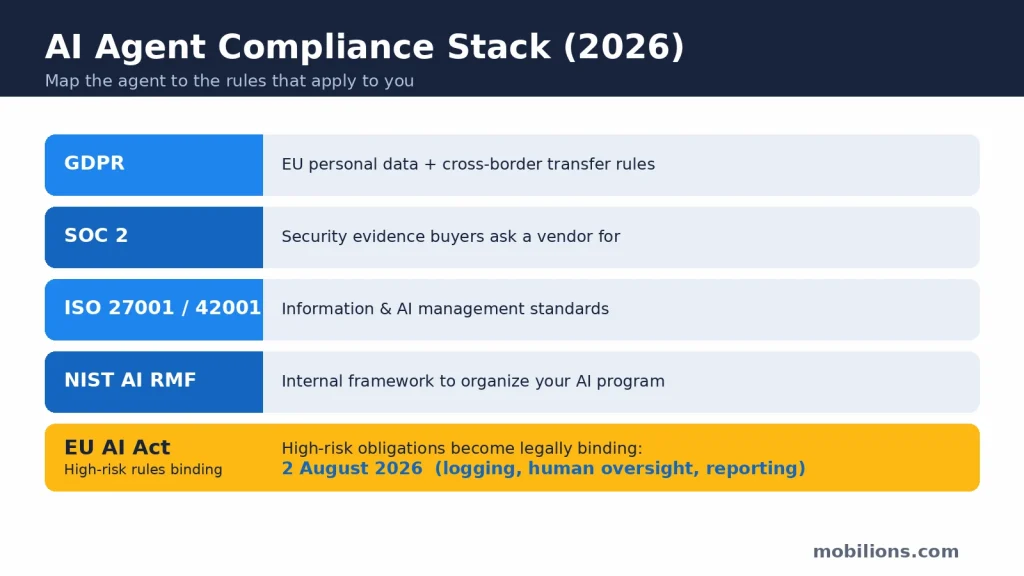
    AI agent compliance stack 2026: GDPR, SOC 2, ISO 27001, NIST AI RMF, and the EU AI Act deadline

    GDPR governs personal data of EU residents, including a hard rule on international transfers (Chapter V) that is triggered every time data crosses a border, which is easy to do accidentally through an AI API. SOC 2 (AICPA) is the external evidence most enterprise buyers ask a vendor for, covering security, availability, and confidentiality controls. ISO 27001 and the AI-specific ISO/IEC 42001 are the international management-system standards. the NIST AI Risk Management Framework is the voluntary framework most enterprises use internally to organize their AI program.

    And the EU AI Act is the big regulatory shift: its obligations for high-risk AI, including incident reporting, log retention, human oversight, and impact assessments, become legally binding on 2 August 2026, as the regulation sets out. In practice, agent governance leans on SOC 2, GDPR, and ISO 27001 for evidence, while NIST AI RMF and the EU AI Act shape the internal program. You do not need all of them; you need the ones that match your customers, data, and jurisdictions, mapped deliberately.

    How to evaluate an AI agent vendor

    If you are buying rather than building, the vendor’s security is your security, so evaluate it properly rather than trusting a marketing page.

    Ask for concrete evidence, not assurances. A current SOC 2 Type II report and ISO 27001 certification are table stakes for enterprise use. Ask directly whether your data is used to train their models (the answer should be no, in writing), where your data is stored and processed (for data-residency compliance), what audit logs you get access to, and how they defend against prompt injection. Push on the security agreement: it should cover data ownership, breach notification, deletion on offboarding, and liability. Watch for red flags, vague answers about data use, no independent certifications, no audit access, or an unwillingness to put commitments in the contract.

    Is SOC 2 alone enough? It is necessary but not sufficient. SOC 2 tells you the vendor has security controls; it does not tell you the agent is scoped to least privilege in your environment, or how it handles your specific regulatory obligations. Treat SOC 2 as a floor, not a finish line.

    Build vs buy, from a security angle

    The build-or-buy decision looks different through a security lens, and it is worth weighing deliberately.

    Buying a mature agent platform means inheriting a vendor’s security investment, certifications, and patch cadence, which is real value, at the cost of trusting their controls, their data handling, and their prompt-injection defences, and accepting the residency and training-data terms they offer. Building (or having a partner build) a custom agent means the data stays in your environment and under your controls, permissions and logging are exactly what you specify, and there is no third-party training-data question, at the cost of owning the security engineering yourself.

    For agents that touch highly sensitive or heavily regulated data, the control of a custom build often wins; for lower-risk, standard workflows, a well-certified vendor is usually the faster, sensible path. Either way, the security requirements are the same, only who implements them changes.

    Data lifecycle: encryption, training, and offboarding

    Security does not end at access; it follows the data through its whole life with the agent.

    Encrypt sensitive data in transit and at rest, and consider what the agent actually needs to see, sometimes it can work on masked or tokenized data rather than the raw records. Control training use contractually and technically, so your data is not absorbed into a model you do not govern. And plan offboarding before you need it: when you stop using an agent or vendor, you should be able to confirm your data is deleted, exports are handled, and access is revoked, cleanly and verifiably. The question “what happens to my data if I stop using this agent” should have a clear answer before you start, not after.

    Incident response and liability

    Even well-secured systems fail sometimes, so plan for it, because improvising during an incident is how a contained problem becomes a reportable breach.

    Have an incident-response plan that treats the agent as a first-class system: how you detect a problem, how you contain it (including the ability to quickly restrict or shut down the agent’s access), how you investigate using the audit trail, and how you meet notification obligations. Liability is a genuinely unsettled area, when an agent takes a harmful unauthorized action, responsibility can sit with the deploying company, the vendor, or both, depending on the contract and the regulation, which is exactly why the security agreement and the human-approval gates matter.

    Some enterprises are now looking at insurance for AI-related risk, though coverage is still maturing. The practical protection is the same as the prevention: least privilege, human approval on high-risk actions, and complete logs.

    A practical checklist to secure an enterprise AI agent

    Pulling it together, here is the short version of AI agent enterprise data security compliance you can actually work from.

    Scope the agent to least-privilege data and tool access. Give it its own identity, not a shared or human account. Require human approval for high-risk or irreversible actions. Log every action to a complete, tamper-resistant audit trail, and monitor it actively. Defend against prompt injection with input and output filtering and defence in depth, and test adversarially.

    Encrypt sensitive data and control whether it trains any model. Map the agent to your applicable frameworks (GDPR, SOC 2, ISO 27001, NIST AI RMF, EU AI Act) and keep the evidence. Vet vendors for certifications, data-use terms, residency, and audit access. And plan incident response and clean offboarding before launch, not after. Do these, and you have covered the ground that almost every incident comes from.

    How Mobilions helps

    We build production AI agents for enterprises, and security and compliance are the core of how we build, not an afterthought bolted on at the end. We scope agents to least privilege by default, give each agent its own identity and complete audit logging, gate high-risk actions behind human approval, and design in defences against prompt injection rather than assuming the model will protect itself.

    We keep your data in your environment where the sensitivity calls for it, control training use, and map the build to the frameworks you answer to, GDPR, SOC 2, ISO 27001, NIST AI RMF, and the EU AI Act, so the agent is defensible to your security team and your auditors. You own the code, the data, and the logs.

    What we will not do is ship an over-permissioned agent with no audit trail to hit a deadline, because that is precisely the agent that becomes an incident.

    The bottom line

    AI agent enterprise data security compliance is now the deciding factor in whether an agent reaches production, and it is a solvable engineering problem, not a reason to avoid agents. The mindset that works is to treat the agent as a powerful new employee with system access: give it the least access it needs, require approval for the risky moves, log everything, defend the language interface it runs on, and map it to the rules that apply to you.

    The threats are real, prompt injection has no complete fix, over-permissioned agents have a large blast radius, and regulation is tightening with the EU AI Act’s high-risk rules landing in August 2026. But every one of them has a known control, and together they are a checklist, not a mystery. Get the controls right and you can deploy agents that are genuinely useful and genuinely safe. Skip them and you are one crafted paragraph away from an incident.

    If you want a straight assessment of how to secure a specific agent for your data and your regulators, that is exactly the conversation our senior engineers have with enterprise teams every week.

    Book a discovery call for an honest review, no obligation. You can also explore our AI agent development services and how we approach applied AI.

    Key takeaways

    • AI agent security is different from ordinary software security because agents act, choose, and can be manipulated through language; treat an agent as a powerful new employee with system access.
    • AI agent enterprise data security compliance rests on six pillars: access control, action control, auditability, data protection, threat defence, and regulatory alignment.
    • Prompt injection is the top risk (OWASP LLM01) and has no complete fix, so defence in depth is the only credible strategy.
    • Least privilege is the foundation: give the agent the narrowest data and tool access, its own identity, and human approval for high-risk actions. It should have less access than the employee who runs it.
    • Log every action to a complete, tamper-resistant audit trail and monitor it actively; most organizations still do not monitor AI end to end.
    • Map the agent to the frameworks that apply, GDPR, SOC 2, ISO 27001, NIST AI RMF, and the EU AI Act, whose high-risk rules take effect 2 August 2026.
    • Vet vendors for SOC 2, data-use and residency terms, and audit access; SOC 2 is a floor, not a finish line. Plan encryption, training-data control, incident response, and clean offboarding before launch.

    Frequently asked questions

    What is AI agent enterprise data security compliance?

    It is the set of controls that keep an autonomous AI agent from leaking data, taking unauthorized actions, or breaking regulations while it operates inside a business. It spans least-privilege access, human approval for risky actions, complete audit logging, defence against prompt injection, data protection, and mapping the agent to applicable laws and standards like GDPR, SOC 2, and the EU AI Act. In short, it is securing and governing an agent that can act, not just read.

    Why is securing an AI agent harder than securing normal software?

    Because an agent acts rather than just returning information, chooses its next step based on a goal rather than a fixed script, and can be manipulated through the same natural-language interface that makes it useful. That combination means its behaviour is not fully predictable and its access can be turned against you, so it needs the kind of oversight you would give a new employee with system access, not the kind you give a static tool.

    What is prompt injection and why does it matter so much?

    Prompt injection is when an attacker hides instructions in content the agent reads, an email, a document, a web page, and the agent follows them, leaking data or taking unauthorized actions. OWASP ranks it the number one risk for LLM applications, and there is no complete fix even with the best current models. It matters because it is the main way an attacker hijacks an agent’s permissions, which is why least privilege and human approval on risky actions are essential.

    Should my AI agent have the same access as my employees?

    No. An agent works faster, at scale, and can be manipulated in ways a person cannot, so it should usually have narrower access than a human in the same role, with the riskiest capabilities removed or gated behind human approval. Giving an agent full employee-level access creates a system that never sleeps, can be tricked with text, and touches everything, which is a large and unnecessary blast radius.

    How do I prevent an AI agent from leaking company data?

    Scope its data access to the minimum it needs (least privilege), give it its own identity so access is controllable and attributable, filter its inputs and outputs, encrypt sensitive data, control whether your data trains any model, and log every action so you can detect and investigate leaks. Most leakage comes from over-broad permissions rather than sophisticated attacks, so tight scoping is the highest-value control.

    Which regulations apply to enterprise AI agents?

    It depends on your data and industry, but the common stack is GDPR (EU personal data, including cross-border transfer rules), SOC 2 (the security evidence buyers ask for), ISO 27001 and ISO/IEC 42001 (management-system standards), NIST AI RMF (internal program framework), and the EU AI Act, whose high-risk obligations become binding on 2 August 2026. Map the ones that match your customers, data, and jurisdictions rather than trying to satisfy all of them.

    Is SOC 2 compliance enough for an AI agent vendor?

    It is necessary but not sufficient. SOC 2 shows a vendor has security controls, but it does not tell you the agent is scoped to least privilege in your environment, whether your data trains their model, where it is stored, or how they defend against prompt injection. Treat SOC 2 as a floor and ask specifically about data use, residency, audit access, and injection defence on top of it.

    How do I audit what my AI agent is doing?

    Log every meaningful action, what it accessed, decided, and did, to a complete, time-stamped, tamper-resistant trail, and pair it with active monitoring that alerts on unusual behaviour. Review continuously through automated monitoring and schedule human reviews for high-stakes agents. Good logs let you investigate incidents, prove compliance to auditors, and improve the system, and the EU AI Act will require this kind of logging for high-risk AI anyway.

    Should I build or buy an AI agent for security reasons?

    Buying gives you a vendor’s security investment and certifications but means trusting their controls, data handling, and terms. Building or having a partner build keeps data in your environment with permissions and logging exactly as you specify and no third-party training question, at the cost of owning the security work. For highly sensitive or regulated data, the control of a custom build often wins; for standard, lower-risk workflows, a well-certified vendor is usually the faster path.

    What happens to my data if I stop using an AI agent?

    That should be settled before you start. A proper agreement specifies that on offboarding your data is deleted, exports are provided, and access is revoked, verifiably. If a vendor cannot clearly explain deletion and offboarding, treat it as a red flag, because unclear data handling at the end often signals unclear handling throughout.

    Does Mobilions build secure, compliant AI agents?

    Yes. We build production agents with least-privilege access, per-agent identity, complete audit logging, human approval on high-risk actions, and designed-in defences against prompt injection, mapped to the frameworks you answer to, GDPR, SOC 2, ISO 27001, NIST AI RMF, and the EU AI Act. You own the code, data, and logs. Book a discovery call for a straight assessment of how to secure an agent for your data and regulators.
  • AI Value, Risks, Mitigation Strategies, and Benefits: A Complete 2026 Guide

    AI Value, Risks, Mitigation Strategies, and Benefits: A Complete 2026 Guide

    AI value, risks, mitigation strategies, and benefits are the four things every leader has to weigh before trusting a real business process to a model. Put simply: AI creates value by doing cognitive work at machine speed and scale; it carries risks like inaccuracy, data exposure, bias, and compliance exposure; those risks are reduced with governance, human review, and the right architecture; and the benefits you actually keep are the measurable outcomes that survive once the risks are under control. This guide treats AI value risks mitigation strategies benefits as one connected decision, because that is exactly how they behave in practice.

    The gap between promise and payoff is real and measurable. In its 2025 State of AI research, McKinsey found that roughly 88 percent of organizations now use AI in at least one business function, yet only about 39 percent could attribute any measurable profit impact to it, and 51 percent had already experienced at least one negative consequence, most often from AI producing something inaccurate. In other words, almost everyone has adopted AI, few can prove it pays, and half have already been burned. The difference between those groups is rarely the model they chose. It is how deliberately they balanced value against risk. I have architected AI systems on both sides of that line, and this guide is the practitioner playbook I wish every client read before the first pilot.

    Key Takeaways

    • Value and benefits are different. Value is the capability AI adds (speed, prediction, personalization, generation). Benefits are the business outcomes you keep after the risks are controlled (lower cost, faster cycles, revenue, retention).
    • The risks are mostly mundane, not science fiction. Inaccuracy, data exposure, bias, cost overruns, and compliance gaps cause far more damage than any runaway robot scenario.
    • Mitigation is a discipline, not a feature. Governance, human oversight, grounded data, evaluation, and monitoring turn a risky demo into a dependable system.
    • You keep the benefit only if you manage the risk. An AI feature that leaks data or gives wrong answers destroys more value than it creates.
    • Regulation is now a hard deadline. Major EU AI Act obligations for high-risk systems apply from 2 August 2026, so compliance is a planning item, not a someday item.
    • Start where value is high and risk is reversible. The safest first wins are internal, low-stakes, and easy to supervise.

    Value and benefits are not the same thing

    The focus keyword for this topic bundles four words together, and two of them, value and benefits, are often treated as synonyms. Keeping them separate is the single most useful mental model I can give you.

    Value is the raw capability AI brings to a task. A model can read a thousand support tickets in a second, draft a first version of almost any document, spot a pattern in data that a human would miss, or hold a natural conversation at 3 a.m. That capability is the value. It exists whether or not you ever profit from it.

    Benefits are what your business actually banks once that capability is put to work safely and at scale. Lower cost per ticket. A sales team that closes faster because research is automated. A product that retains users because it feels personal. Benefits are downstream of value, and they only appear after the risks between the two have been handled. Plenty of companies have captured AI value in a flashy demo and captured zero benefit in production, because the thing that worked on stage was too unreliable, too expensive, or too risky to ship.

    Holding this distinction in mind changes how you evaluate every AI opportunity. You stop asking only “what can this model do?” and start asking “what outcome will survive contact with real users, real data, and real risk?”

    AI Value Risks Mitigation Strategies Benefits at a Glance

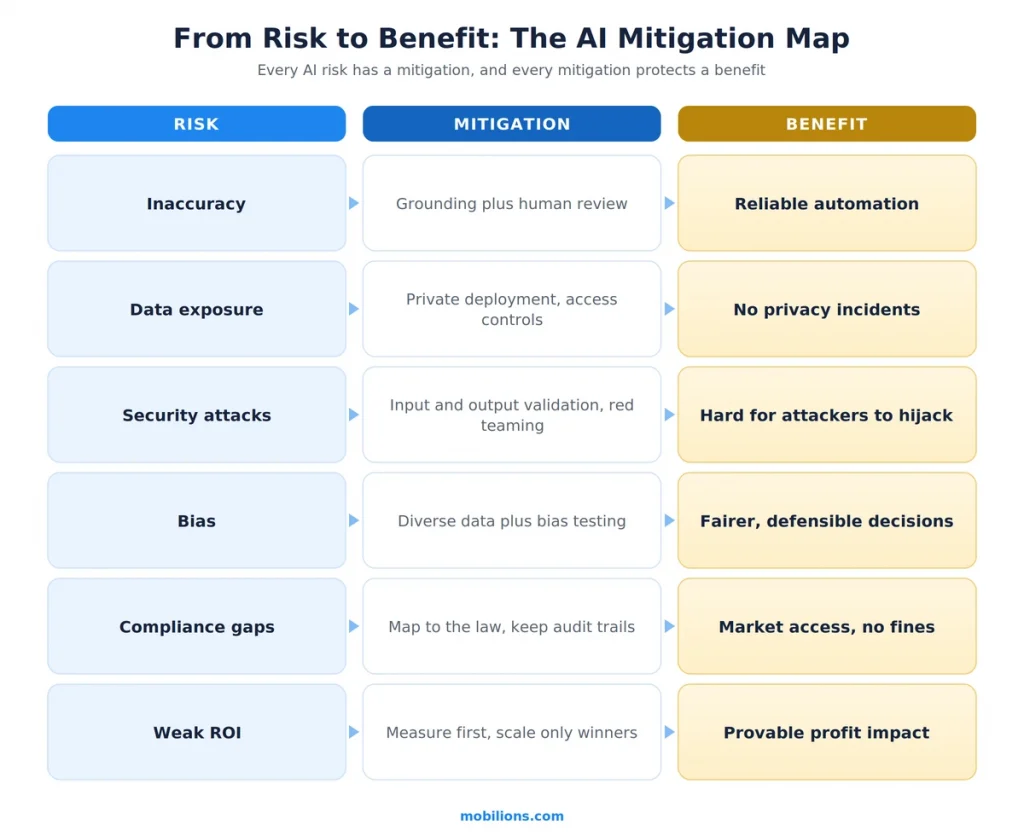
    AI risk to mitigation to benefit map for business

    Before we go deep, here is the whole argument in one table. Each row takes a real risk, explains why it matters, gives the mitigation that works, and names the benefit you keep when you get it right.

    RiskWhy it mattersMitigation strategyBenefit you keep
    Inaccuracy (hallucination)Wrong answers erode trust and can cause real harmGround the model in your own data, add human review on high stakes outputReliable automation people actually trust
    Data exposureSensitive data sent to a model can leak or be retainedPrivate deployment, redaction, strict access controlsAutomation without a privacy incident
    Security attacksPrompt injection and misuse can hijack an AI featureInput and output validation, red teaming, least privilegeA feature attackers cannot easily turn against you
    Bias and unfairnessSkewed outputs create legal and reputational damageDiverse data, bias testing, documented decisionsFairer outcomes and defensible decisions
    Compliance gapsNew laws carry heavy fines for high-risk usesMap uses to regulation, keep records and audit trailsMarket access and no regulatory surprises
    Cost and weak ROIRunaway inference cost and failed pilots waste budgetMeasure value first, monitor spend, scale only winnersProfit impact you can actually show
    Vendor lock-inTotal dependence on one model is fragileAbstraction layer, multi-model design, exit planFlexibility and negotiating power

    The rest of this guide expands each of these four pillars: the value, the risks, the mitigation strategies, and the benefits.

    The value AI creates

    AI value comes from a small number of capabilities that repeat across almost every industry. Understanding them helps you spot where AI is genuinely useful and where it is being oversold.

    The first source of value is automation of cognitive work. Tasks that used to need a person to read, classify, summarize, or route can now run continuously and instantly. This is where most early value shows up, because the work is high volume and the rules are fuzzy enough that traditional software struggled with it.

    The second is better decisions from data. Models find patterns in demand, churn, fraud, and risk that rule based systems miss. The value here is not a fancy dashboard. It is a decision made earlier and more accurately than a human team could manage alone.

    The third is personalization at scale. A model can tailor a recommendation, a message, or an experience to one person, then do it again for a million people. Done well, this is one of the strongest drivers of retention and revenue.

    The fourth is generation. Drafting text, code, images, and structured content collapses the time from blank page to first version. The value is speed of creation, not finished quality, which matters for how you supervise it.

    The fifth is availability. AI does not sleep, take breaks, or have a bad Monday. For support, monitoring, and always on services, that consistency is itself the value.

    McKinsey’s research lines up with what I see in the field: about 64 percent of organizations say AI is helping them innovate, and nearly half report gains in customer satisfaction and competitive differentiation. Notice that these are qualitative wins. They are real, but they are not the same as proven profit, which brings us to the honest part.

    Where AI value is overstated

    Value is real, but it is not evenly distributed. AI is weak wherever the cost of a wrong answer is high and hard to catch, wherever the task needs true understanding rather than pattern matching, and wherever your data is thin or messy. A model is only as good as the context you give it. If your knowledge lives in people’s heads and scattered files, an AI tool will produce confident nonsense until you fix the data underneath it. Treating AI as a magic layer on top of a broken process is the fastest way to capture value in a demo and lose it in production.

    The risks of AI, and why most of them are mundane

    When people picture AI risk, they imagine dramatic scenarios. The risks that actually hurt businesses are far more ordinary, and that is good news, because ordinary risks can be managed with ordinary discipline. Frameworks like the NIST AI Risk Management Framework exist precisely to bring this discipline into everyday practice. Here are the risks that matter.

    Inaccuracy and hallucination. A model can state something false with complete confidence. McKinsey found inaccuracy to be the single most common negative consequence organizations reported, hitting nearly a third of respondents. In a support bot this is embarrassing. In healthcare, finance, or legal work it can be dangerous.

    Data privacy and exposure. Every prompt is data leaving your control. Paste a customer list or source code into a public model and you may have created a privacy incident or leaked intellectual property. This is one of the most common and most avoidable mistakes I see.

    Security attacks. AI features open a new attack surface. The OWASP Top 10 for LLM Applications puts prompt injection at the top, where a crafted input tricks the model into ignoring its instructions, revealing data, or taking actions it should not. Insecure output handling, sensitive information disclosure, and excessive agency round out the list.

    Bias and unfairness. A model trained on skewed data will make skewed decisions, and it will do so at scale and with a false air of objectivity. In hiring, lending, and any regulated decision, that is both an ethical problem and a legal one.

    Compliance and regulation. The rules are no longer optional. The EU AI Act entered into force in 2024, prohibited certain practices from February 2025, and applies most of its obligations for high-risk AI systems from 2 August 2026. If you serve EU users or partners, that date is a planning deadline, not a distant possibility.

    Cost and weak return. AI can quietly burn money. Inference costs scale with usage, pilots stall before they reach production, and teams pay for capability they never convert into benefit. This is why only 39 percent of organizations in McKinsey’s study could point to any profit impact from AI at all.

    Concentration and vendor lock-in. Building everything on a single provider’s model feels fast at first and fragile later. Prices change, models get deprecated, terms shift, and you are exposed to all of it with no alternative ready.

    Mitigation strategies that actually work

    Mitigation is where value becomes benefit. The most useful way I have found to organize it is the four functions of the NIST AI Risk Management Framework: Govern, Map, Measure, and Manage. They turn a vague sense of caution into concrete steps.

    Govern: set the rules before the pilot

    Governance is deciding, in advance, what AI is allowed to do in your organization and who is accountable when it goes wrong. That means a short written policy on what data can and cannot go into a model, which use cases need human sign off, and who owns each AI system. This sounds like paperwork, but it is the cheapest risk control you will ever put in place. Most AI disasters trace back to a decision that no one was clearly responsible for. Governance also includes a clear approval path so teams do not quietly ship a high-risk feature without review.

    Map: know where the risk actually lives

    Before mitigating, identify what could go wrong for a specific use case. A model that drafts internal meeting notes carries almost no risk. The same model answering medical questions for the public is a different animal. Mapping means classifying each use by the stakes involved: how bad is a wrong answer, what data does it touch, and can a human catch a mistake before it causes harm. This single habit stops teams from applying heavy controls to harmless tools and, more importantly, from shipping dangerous ones with no controls at all.

    Measure: test, evaluate, and monitor

    You cannot manage what you do not measure. Before launch, build an evaluation set of real questions with known good answers and score the model against it, so quality is a number rather than a vibe. Test for the specific failure modes that matter, including the security cases on the OWASP list, with adversarial or red team prompts that actively try to break the system. After launch, monitor accuracy, cost, and unusual behavior continuously, because a model that behaved yesterday can drift tomorrow as inputs change.

    Manage: human oversight and graceful failure

    The final function is keeping humans in the loop where it counts and designing systems that fail safely. For high stakes output, a person reviews before anything reaches a customer or a permanent record. This is the core idea behind designing AI to support human workflows rather than replace human judgment wholesale. Ground the model in your own trusted data so it answers from facts instead of guessing, keep sensitive workloads on private or custom AI deployments where you control the data, and add an abstraction layer so you can switch models without rebuilding the product. When the model is unsure, the right behavior is to escalate to a human, not to invent an answer.

    McKinsey’s data shows this discipline is spreading: organizations now actively work to mitigate an average of four AI-related risks, up from two in 2022. The companies pulling ahead are not the ones using the most AI. They are the ones managing it best.

    The benefits you keep when risk is handled

    Once mitigation is in place, the value you captured turns into benefits you can bank. These are the outcomes that survive production.

    Lower cost per outcome. Automating high volume cognitive work reduces the cost of each ticket, each document, each review, without cutting the corners that create risk.

    Faster cycle times. Research, drafting, and analysis that took days can take minutes, so teams ship and respond faster. Speed compounds across a whole organization.

    Higher quality and consistency. A well supervised AI system applies the same standard every time and never has an off day, which raises the floor on quality even when it does not raise the ceiling.

    Revenue and retention. Personalization and always on service keep customers engaged and buying, which is where AI most reliably touches the top line.

    Resilience and focus. When AI handles the repetitive load, your best people spend their time on the judgment calls, relationships, and creative work that machines cannot do. That is a benefit to morale as much as to output.

    The through line is trust. Every one of these benefits depends on people trusting the system enough to rely on it, and that trust is exactly what good mitigation buys you.

    A simple framework for weighing value against risk

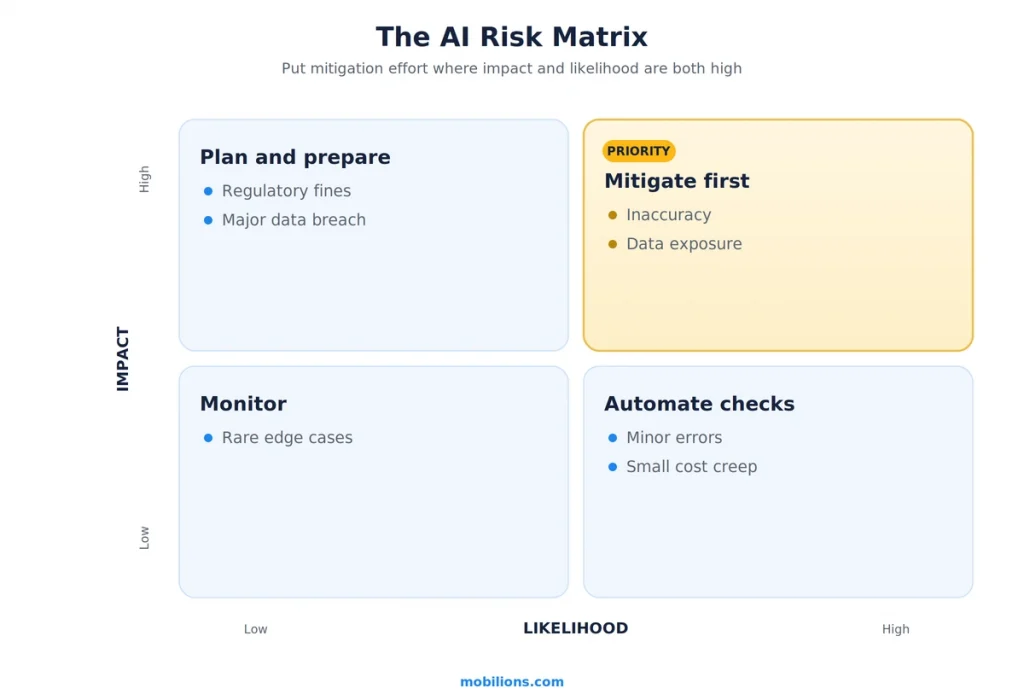
    AI risk matrix by impact and likelihood

    You do not need a committee to decide where to start. For any AI opportunity, score it on two axes and act accordingly.

    First, value potential: how much time, cost, or revenue is genuinely at stake if this works? Second, risk level: how bad is a wrong answer, how sensitive is the data, and how hard is a mistake to catch and reverse?

    High value and low risk is where you start. These are the internal, low stakes, easy to supervise use cases like drafting, summarizing, and internal search, and they let your team build skill safely. High value and high risk is worth doing, but only with the full mitigation stack: governance, human review, grounding, and monitoring. Low value use cases, at any risk level, can wait no matter how impressive the demo looks. The reversibility test matters most: if a mistake is cheap to catch and undo, you can move fast; if it is not, you slow down and add oversight until it is.

    Real-world scenario: an AI customer-support assistant

    Consider a company that wants an AI assistant to handle customer support, the single most common AI project I am asked to build.

    The value is obvious. The assistant can answer common questions instantly, at any hour, in any language, and free the human team for hard cases. The risks are just as clear. It could give a confidently wrong answer about a refund policy, it could expose one customer’s data to another, and it could be manipulated by a crafted prompt into ignoring its rules.

    Here is where mitigation earns its keep. We ground the assistant only in the company’s approved help content, so it answers from real policy rather than guessing. We add strict data controls so it never sees more than the current customer’s information. We validate inputs and outputs against the common attack patterns and red team it before launch. And we design it to escalate to a human the moment it is unsure or the stakes are high, such as anything involving money or account changes.

    The benefit the company keeps is a support operation that resolves most routine questions instantly at a fraction of the cost, with customer trust intact and the human team focused on the cases that need them. Same model, same use case. The only reason it delivers benefit instead of a headline is the mitigation layer between the value and the risk.

    Common mistakes and myths

    Mistake: sending sensitive data to a public model. The convenience is not worth the exposure. Decide what data is allowed near a model before anyone starts pasting.

    Mistake: no measurement before scaling. Teams fall in love with a demo and roll it out with no baseline, then cannot tell whether it helped. Measure value on a small use case first.

    Mistake: treating mitigation as a launch blocker instead of a design input. Bolted on controls are weak and slow. Build governance and oversight into the system from day one.

    Myth: bigger model means better outcome. Past a point, the constraint is your data and your process, not the size of the model. A smaller model grounded in good data beats a giant one guessing.

    Myth: AI will replace the whole team. In practice the reliable pattern is augmentation. AI handles volume and speed, humans handle judgment, exceptions, and relationships.

    Myth: the real risk is science fiction. The dangerous risks are ordinary and near term: a wrong answer, a data leak, a compliance miss. Those are the ones that cost real money, and the ones you can actually control.

    Why Mobilions

    Balancing AI value against AI risk is not a research exercise. It is an engineering and governance discipline, and it is what we do. Mobilions has delivered software since 2016, with more than 250 projects completed for over 100 clients across more than 20 countries. We build AI features the way this guide describes: grounded in your own data, wrapped in the right controls, measured against real outcomes, and designed so a human stays in the loop wherever the stakes are high. If you want AI that produces benefits you can prove rather than demos you cannot ship, our AI development team can help you map the value, contain the risk, and build the system properly. You can also explore custom software development or hire dedicated AI engineers to extend your own team.

    Summary

    AI value, risks, mitigation strategies, and benefits are four parts of one decision. The value is the capability AI adds: automation, better decisions, personalization, generation, and constant availability. The risks are mostly ordinary: inaccuracy, data exposure, security attacks, bias, compliance gaps, weak ROI, and vendor lock-in. The mitigation strategies that work follow the NIST pattern of govern, map, measure, and manage, expressed as clear policy, honest risk classification, real evaluation and monitoring, and human oversight with grounded data. And the benefits you keep, lower cost, faster cycles, higher quality, revenue, retention, and resilience, appear only when the mitigation layer holds. Most organizations have adopted AI. Far fewer have profited from it. The gap is not the model. It is the discipline of managing value and risk together, and that discipline is entirely within your reach.

    Frequently asked questions

    What is the difference between AI value and AI benefits?

    Value is the capability AI adds to a task, such as reading data fast or drafting content instantly. Benefits are the business outcomes you keep once that capability runs safely in production, such as lower cost, faster cycles, or higher retention. Value exists in a demo. Benefits exist on your income statement, and only after the risks between the two are controlled.

    What are the main benefits of AI adoption?

    Lower cost per outcome, faster cycle times, more consistent quality, higher revenue and retention through personalization and constant availability, and a team freed to focus on judgment and creative work. These benefits are real, but they only materialize when risk is managed. Unmanaged AI often costs more than it saves.

    What are the biggest risks of using AI in business?

    The most common and damaging risks are inaccuracy (the model stating something false with confidence), data exposure (sensitive information leaving your control), security attacks like prompt injection, bias in automated decisions, compliance gaps under new laws, weak or unproven return on investment, and over dependence on a single vendor. In McKinsey’s 2025 research, inaccuracy was the most reported negative consequence.

    What is the real cost of getting AI wrong?

    It is rarely a dramatic failure and usually a slow one: wasted spend on tools that never reach production, a confident wrong answer that damages trust, a data leak, or a compliance fine. Research finds most AI value never lands because risk and integration were ignored. The cost of getting it wrong is mostly the value you never capture.

    What does risk mitigation actually mean for AI?

    Risk mitigation means reducing the chance or the impact of something going wrong, before it does. For AI, it is the set of controls that sit between a capable model and a dependable system: clear policy, testing, human oversight, grounding in trusted data, and monitoring. It does not remove risk, it makes it manageable and reversible.

    What are the 4 types of risk mitigation?

    The four classic responses are avoid (do not use AI where the risk outweighs the value), reduce (add controls like human review and evaluation), transfer (shift risk through contracts, insurance, or a vendor’s guarantees), and accept (knowingly proceed with a small, monitored risk). Most AI programs use a mix, matched to how high the stakes are.

    How do you mitigate AI risks?

    Follow the NIST AI Risk Management Framework: govern (set clear policy and accountability), map (classify each use by its stakes and data), measure (test, red team for security, and monitor after launch), and manage (keep humans in the loop on high stakes output, ground the model in trusted data, and design for safe failure). Together these turn a risky demo into a dependable system.

    How do you implement AI safely?

    Start with a low-stakes, reversible use case, ground the model in your own trusted data, test it against a real evaluation set, and keep a human reviewing high-stakes output. Add a data policy so sensitive information stays private, then monitor after launch. Safe implementation is about controls and staged rollout, not moving slowly for its own sake.

    How do you audit the AI tools your team is using?

    List every AI tool in use, including the unofficial ones staff adopted on their own. For each, check what data it touches, where that data goes, whether outputs are reviewed, and whether it meets your compliance needs. This shadow AI audit usually surfaces the biggest hidden risk: sensitive data flowing into public tools with no oversight.

    What happens if AI makes a wrong decision in your business?

    You remain accountable, not the model. That is why high-stakes AI output needs a human in the loop, an audit trail, and a clear owner. A wrong AI decision that reaches a customer can cost money, trust, and compliance standing. Mitigation exists so that wrong outputs are caught before they act, not explained after.

    How do you balance AI with human judgment?

    Let AI handle volume and speed, and keep humans on judgment, exceptions, and anything high-stakes. The pattern is human in the loop for consequential decisions and human on the loop for monitored routine ones. Over-reliance is its own risk, so design the workflow so people stay accountable and can always override the model.

    What is the biggest AI risk companies overlook?

    Data exposure through everyday use. Employees paste sensitive customer data, source code, or strategy documents into public models to save time, often with no policy telling them not to. It is one of the most common and most preventable risks, and it is fixed with a clear data policy and a private deployment for sensitive work.

    How does AI regulation affect my business in 2026?

    If you touch EU users or partners, the EU AI Act matters now. Prohibited practices have applied since February 2025, and most obligations for high-risk AI systems apply from 2 August 2026. That makes compliance a current planning item. Map your AI uses to the law’s risk tiers, keep documentation and audit trails, and treat high-risk uses with extra care.

    How do you measure the value or ROI of AI?

    Pick one use case, set a baseline for the metric that matters (cost per ticket, hours per report, conversion rate), run the AI system, and compare. Only 39 percent of organizations can currently attribute profit to AI, largely because they scaled before they measured. Measuring a small win first is how you avoid joining them.

    Is AI worth the risk for small businesses?

    Yes, if you start where value is high and risk is reversible. Internal, low stakes uses like drafting, summarizing, and internal search let a small team capture real value with almost no downside. Save the high risk, customer facing, or regulated uses for after you have built experience and put basic controls in place.

    Will AI replace my team, or just change how they work?

    For most roles it changes the work rather than removing it. AI takes over repetitive tasks, and people move up to judgment, review, and the exceptions AI cannot handle safely. The teams that benefit treat AI as a tool their people direct and check, not a replacement, and they reskill rather than simply cut.

    Can you get AI benefits without taking on risk?

    Not entirely, but you can shrink the risk until the benefit clearly outweighs it. That is the whole point of mitigation. By choosing low risk use cases first, grounding models in your own data, keeping humans in the loop, and measuring outcomes, you capture most of the benefit while holding the risk to a level you can manage and reverse.