Tag: mobile app development cost

  • Enterprise Mobile App Development: The Complete 2026 Guide

    Enterprise Mobile App Development: The Complete 2026 Guide

    Enterprise mobile app development is what happens when a mobile app has to answer to an IT department, a security team, and a compliance auditor, not just an app store reviewer. It is a different discipline from building a consumer app, and treating the two the same is the fastest way to blow a budget and a deadline.

    This guide explains what makes enterprise mobile app development different, how the build actually works, what the stack looks like in 2026, how apps get distributed through MDM instead of public stores, and what all of it costs. It is written from the perspective of engineers who scope, build, and support these systems in production.

    What is enterprise mobile app development?

    Enterprise mobile app development is the process of building mobile applications for internal business use, such as field operations, logistics, sales enablement, or employee tools, that must integrate with existing company systems and meet strict security and compliance requirements.

    The users are employees, partners, or vetted customers, not the open public. That single fact changes almost everything: how the app authenticates people, where it gets its data, how it is distributed, and how it is governed after launch.

    A consumer app optimizes for downloads and delight. An enterprise app optimizes for reliability, security, and fit with the systems a business already runs. Both are mobile apps. Only one has to pass a SOC 2 audit.

    Why enterprise mobile apps are different from consumer apps

    The gap shows up in four places, and each one adds cost and engineering care that a consumer app never sees.

    Security is a first-class requirement, not a feature. Enterprise mobile apps carry role-based access control, single sign-on through SSO or LDAP, encrypted local storage, and often certificate pinning. Security work typically adds 15 to 30 percent to a development budget, and that is money well spent rather than overhead.

    They integrate with legacy systems. An enterprise app rarely stands alone. It has to talk to an ERP, a CRM, a data warehouse, or a decades-old internal API that was never designed for mobile. This integration depth, not the number of screens, is usually the biggest driver of cost and timeline.

    They are governed after launch. Consumer apps ship and iterate freely. Enterprise apps live under IT policy: managed updates, remote wipe, device compliance checks, and audit trails. The app has to cooperate with that governance from day one.

    They run at organizational scale with offline realities. Warehouse floors, hospital basements, and remote sites have poor connectivity, so offline mode and reliable sync are common requirements rather than nice-to-haves.

    Enterprise mobile application development services: what you actually get

    When you hire a team for enterprise mobile application development, the deliverable is not just an app binary. It is a system that IT can trust and operate.

    A complete service covers discovery and security scoping, UX for real workflows rather than marketing screens, the mobile app itself, the backend and integration layer, and the deployment and support model. The integration layer, connecting the app to your ERP, CRM, identity provider, and data systems, is often where most of the real engineering lives.

    Good enterprise mobile app development services also include the unglamorous parts: role and permission modeling, audit logging, compliance documentation, and a rollout plan. These are the things that decide whether the app is adopted or abandoned.

    The point of naming this clearly is simple. If a vendor quotes you only for screens and features, they have not scoped the enterprise part of enterprise mobile app development, and the number will move once reality arrives.

    How to build enterprise mobile apps: the process

    Knowing how to build enterprise mobile apps is mostly about doing the hard thinking before writing code. The process we use runs in five stages.

    Discovery and security scoping. Map the workflows, the systems the app must integrate with, the compliance regime (HIPAA, SOC 2, ISO 27001, GDPR), and the device and distribution model. This is where the true scope, and the honest cost, becomes visible.

    Architecture. Decide the integration approach, the offline and sync strategy, the identity model (SSO, LDAP, OAuth), and the platform choice. Cross-platform frameworks like Flutter and React Native are common here because they cut the cost of shipping to both iOS and Android.

    Development. Build the app, the backend, and the integration layer in parallel, with security controls baked in rather than bolted on. Role-based access, encrypted storage, and audit logging are written as the app is written.

    Security testing and hardening. Enterprise apps get a dedicated security pass, penetration testing, and a hardening phase. Budget roughly 4 to 8 weeks and $15,000 to $40,000 for thorough enterprise security testing on a serious app.

    Deployment and support. Package the app for MDM distribution, plan the rollout, train users, and stand up ongoing support. The launch is the start of the app’s life, not the end of the project.

    The technology stack for enterprise mobile apps

    There is no single correct stack, but enterprise choices cluster around a few sensible defaults in 2026.

    On the client, cross-platform frameworks (Flutter, React Native) dominate internal apps because one codebase serving iOS and Android roughly halves the build and maintenance cost. Native (Swift, Kotlin) is chosen when the app needs deep device features or maximum performance.

    On the backend, teams reach for well-supported, boring-in-a-good-way choices: Node.js, Python, Java, or Go, with PostgreSQL or a managed cloud database, running on AWS, Azure, or Google Cloud. The premium is on reliability and support, not novelty.

    For identity and security, the stack includes an enterprise identity provider (Okta, Microsoft Entra, or the company’s existing directory), SSO and LDAP integration, and mobile security controls aligned to the OWASP Mobile Application Security standard. Our mobile app development and custom software development teams treat this integration middleware, which connects the app to the ERP and CRM systems the business already runs, as the core of the build.

    Enterprise mobile app distribution and MDM deployment

    Here is the difference that surprises teams new to this: enterprise apps usually do not ship through the public App Store or Google Play. They are distributed privately through Mobile Device Management.
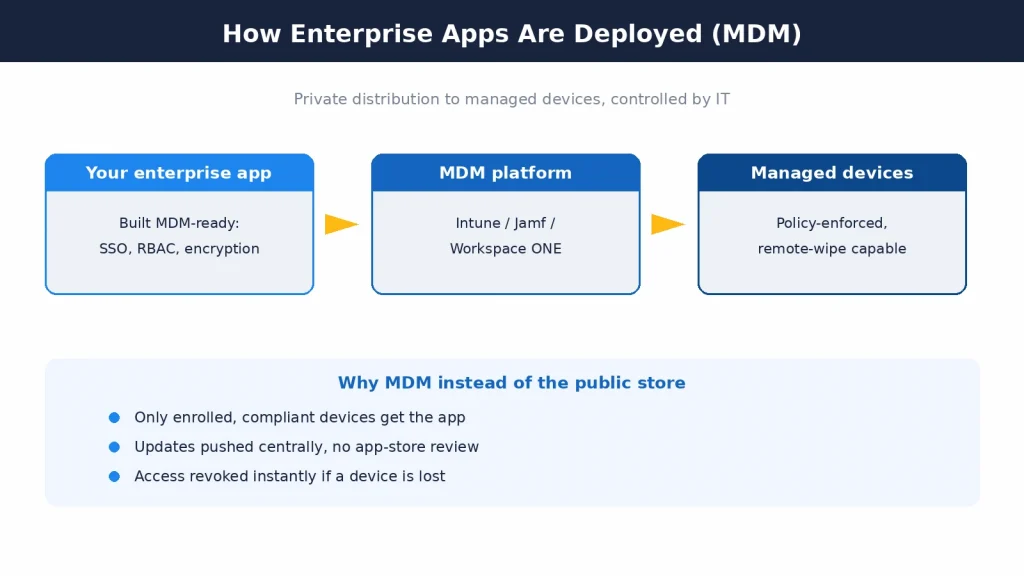
    How enterprise mobile apps are deployed through MDM by Mobilions

    Enterprise mobile app distribution runs through MDM platforms such as Microsoft Intune, VMware Workspace ONE, or Jamf, paired with Apple Business Manager and Android Enterprise. The app is pushed to managed devices, configured by policy, and updated centrally, with the ability to remotely wipe it if a device is lost.

    This MDM enterprise app deployment model is what lets IT enforce compliance: only enrolled, policy-compliant devices get the app, and access can be revoked instantly. It also means your enterprise mobile app development platform choices have to be MDM-compatible from the start, because retrofitting management support later is painful.

    Practically, MDM integration and setup adds roughly $5,000 to $15,000 to a project, depending on the platform and how many device types need management policies. That is a small line item next to the adoption and security it buys.

    How much does enterprise mobile app development cost in 2026?

    Cost scales with compliance burden and integration depth far more than with screen count. With that framing, 2026 numbers fall into three honest bands.
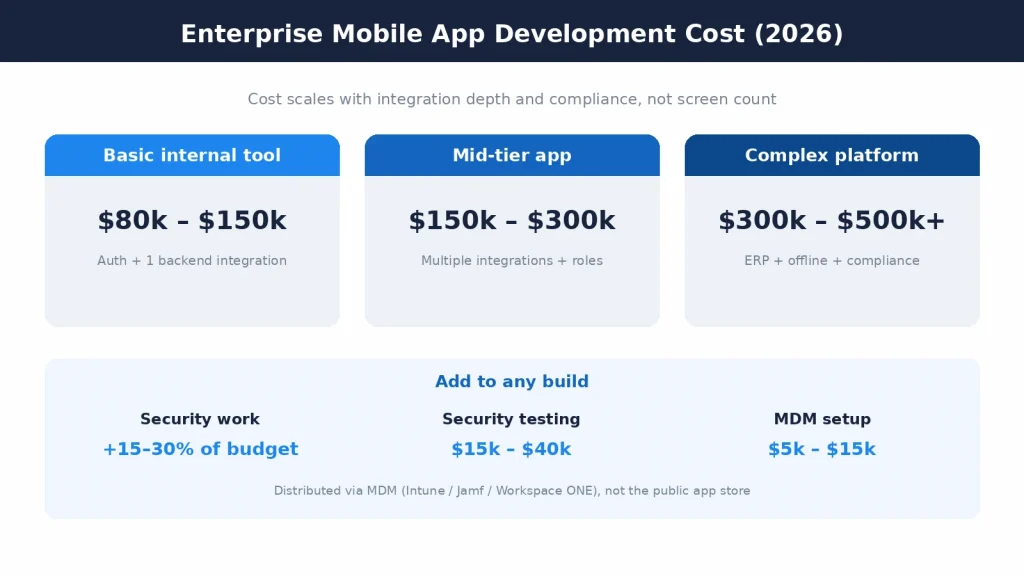
    Enterprise mobile app development cost bands for 2026 by Mobilions

    A basic internal tool, with authentication and a single backend integration, runs about $80,000 to $150,000. A mid-tier app, with multiple integrations and user roles, runs about $150,000 to $300,000. A complex platform, with ERP integration, offline mode, and formal compliance, runs $300,000 to $500,000 and can pass $1,000,000 for the largest programs.

    Inside those totals, security work adds 15 to 30 percent, dedicated security testing adds $15,000 to $40,000, and MDM setup adds $5,000 to $15,000. None of these are places to cut, because they are the parts that make the app safe to deploy across an organization.

    The most useful thing you can do for your budget is scope the integrations and compliance early. That is where enterprise mobile app development costs are made or blown, and a vendor who scopes them honestly will save you far more than one who quotes a low number and discovers the ERP later.

    Build versus buy: when a custom enterprise app makes sense

    Not every internal need justifies a custom build, and an honest enterprise mobile app development partner will tell you when to buy instead.

    Off-the-shelf software wins when your process is standard and a mature product already fits it, such as generic expense tracking or standard field-service ticketing. You get it faster and cheaper, and someone else maintains it. Forcing a custom build on a solved problem is a waste of budget.

    Custom enterprise mobile app development wins when the workflow is your competitive edge, when integration with your specific systems is deep, or when compliance and data control rule out a shared SaaS product. If the app has to bend to your ERP and your rules rather than the other way around, buying rarely works.

    The middle path is common: buy the commodity pieces and build the parts that are truly yours, connected through an integration layer. The decision should come from the workflow and the integration depth, not from a preference for building. Scope it honestly and the answer is usually clear before a line of code is written.

    Choosing an enterprise mobile app development company

    The right enterprise mobile app development company is one that talks about your systems and your security before it talks about screens. That is the fastest signal of whether they have done this before.

    Look for real integration experience with ERP, CRM, and identity systems, a documented security and compliance track record, and a support model that lasts beyond launch. Ask how they handle MDM distribution and managed updates, because a team that has shipped enterprise apps will have a clear answer. If you need to scale a team quickly, you can also hire mobile developers who already work this way.

    Be cautious of quotes that price only the visible app. A serious enterprise mobile application development company scopes the integration layer, the security work, and the rollout, and it will tell you when your requirements push the project into a higher cost band rather than discovering it mid-build.

    Ownership matters too. You should own the code, the infrastructure, and the roadmap. A good partner builds the app to hand it over, not to lock you in.

    A quick example: what an enterprise build looks like in practice

    Consider a logistics company that wants a driver and warehouse app. It needs to work offline in low-signal areas, sync when connectivity returns, read and write to the existing ERP, authenticate staff through the company’s identity provider, and deploy to company-owned devices only.

    The scope decisions follow directly. Cross-platform on Flutter to cover both device types cheaply. An integration layer between the app and the ERP so the app never talks to the ERP directly. Offline-first data with conflict-safe sync. SSO through the existing directory, role-based access for drivers versus supervisors, and audit logging for compliance.

    Distribution goes through Intune, not the public store, so IT controls who has the app and can wipe a lost device. On these requirements the project lands in the mid-to-complex band, and the integration and offline work, not the screen count, is what sets the price.

    Notice what drove every decision above: not the number of screens, but the systems the app had to touch and the environment it had to survive. Change the ERP or the connectivity and the estimate changes with it. That is enterprise mobile app development in one concrete picture, and it is why honest scoping beats a low quote every time.

    Core features that define enterprise mobile applications

    Certain capabilities show up in almost every serious build, and together they are what separate enterprise mobile applications from ordinary apps. Knowing them helps you scope realistically and judge a vendor’s quote.

    Role-based access control comes first. Different employees see and do different things, so the app models roles and permissions rather than treating every user the same. This alone touches the UI, the backend, and the audit layer.

    Single sign-on is expected, not optional. Employees should sign in with the same identity they use for everything else, through SSO, LDAP, or OAuth against the company directory, so there is no separate password to manage or leak.

    System integration is usually the heart of the app. Enterprise apps read and write to ERP, CRM, and data platforms, and that integration layer is where most of the engineering time goes. Offline mode and reliable sync sit alongside it, because real work happens in places with poor connectivity.

    Finally, audit logging, encrypted storage, and MDM compatibility round out the baseline. These are the controls that let a security team sign off and an auditor tick the box, and they are the reason enterprise mobile app development is scoped differently from a consumer build.

    Compliance and industry considerations

    The compliance regime an app falls under changes the scope more than almost any feature decision, so it belongs in the first conversation, not the last.

    In fintech, enterprise mobile app development carries PCI DSS obligations, strong authentication, transaction integrity, and audit trails, and the security bar is high because the data is money. Anything touching payments or account data is scoped as sensitive from the start.

    In healthcare, HIPAA governs how patient data is stored, transmitted, and accessed, which pushes encryption, access logging, and strict role controls to the front. An app that handles protected health information is a compliance project with a mobile front end, not a mobile project with a compliance checkbox.

    In logistics and field operations, the pressure is less about regulation and more about reliability: offline-first behavior, device durability, and clean ERP sync. Different industries stress different parts of the same discipline, which is why a team that has shipped in your sector scopes faster and more honestly.

    The common thread is that compliance and integration depth, taken together, set the true size of an enterprise build. A vendor who asks about your regulatory environment early is protecting your budget, not padding it.

    Common mistakes that derail enterprise mobile app projects

    Most enterprise mobile app development trouble is predictable, and nearly all of it traces back to scoping the wrong things.

    The first mistake is pricing screens instead of integrations. The visible app is the cheap part; the ERP, CRM, and identity connections are where the effort lives. A quote that ignores them will be wrong, and the correction always arrives mid-build when it is most expensive.

    The second is treating security and compliance as a final phase. Retrofitting encryption, role-based access, and audit logging into a finished app costs far more than building them in, and it often forces a redesign. Security scoped late is security done twice.

    The third is ignoring distribution until the end. If the app was not built to be MDM-compatible, packaging it for managed deployment becomes its own mini-project. Distribution is an architecture decision, not a launch-day task.

    The fourth is skipping the rollout and training plan. An enterprise app that nobody adopts is a total loss regardless of how well it is built, and adoption depends on a real rollout, not a launch email. The engineering is only half the job; getting the app onto devices and into daily use is the other half.

    Frequently asked questions

    What is enterprise mobile app development?

    Enterprise mobile app development is building mobile apps for internal business use that integrate with company systems like ERP and CRM, enforce enterprise security and access controls, and meet compliance requirements. The users are employees or vetted partners rather than the general public.

    How to build enterprise mobile apps?

    Choose a company that scopes your integrations, security, and rollout before pricing screens, has real ERP, CRM, and identity integration experience, documents its security and compliance work, offers support beyond launch, and hands you full ownership of the code and infrastructure.

    How much does enterprise mobile app development cost in 2026?

    A basic internal tool costs about $80,000 to $150,000, a mid-tier app with multiple integrations and roles about $150,000 to $300,000, and a complex platform with ERP integration, offline mode, and compliance $300,000 to $500,000 or more. Security adds 15 to 30 percent and MDM setup adds $5,000 to $15,000.

    How long does it take to build an enterprise mobile app?

    A basic internal tool can take a few months; a mid-tier app with several integrations typically runs four to eight months; a complex compliant platform can run eight months or more. Security testing alone adds roughly four to eight weeks.

    How do we choose an enterprise mobile app development company?

    How do we choose an enterprise mobile app development company?

    Why are enterprise mobile apps more expensive than consumer apps?

    Because cost scales with compliance and integration depth, not screen count. Enterprise apps must connect to legacy systems, enforce role-based security and SSO, support offline use, pass security testing, and deploy under IT governance, all of which a consumer app skips.

    What is MDM enterprise app deployment?

    MDM (Mobile Device Management) enterprise app deployment distributes an app privately to managed devices through platforms like Microsoft Intune, VMware Workspace ONE, or Jamf, rather than the public app stores. It lets IT enforce device compliance, push updates centrally, and remotely wipe the app if a device is lost.

    Should we build native or cross-platform for an enterprise app?

    Cross-platform frameworks like Flutter and React Native are the common default for internal enterprise apps because one codebase for iOS and Android roughly halves build and maintenance cost. Native is worth it when the app needs deep device features or maximum performance.

    Build an enterprise app that IT will actually trust

    Enterprise mobile app development succeeds or fails on the parts users never see: the integrations, the security, and the deployment. If you are scoping an internal app and want an honest read on cost, timeline, and stack, talk to Mobilions. Senior engineers scope it, build it, ship it through your MDM, and support it in production.
  • Healthcare Mobile App Development: A Complete 2026 Guide

    Healthcare Mobile App Development: A Complete 2026 Guide

    Healthcare mobile app development is the process of building iOS or Android apps that handle patient or clinical data, which means HIPAA compliance, strong security, and often EHR integration are part of the job from day one, not features you bolt on later. A basic HIPAA-ready MVP typically starts around $60,000 and ships in about four to six months. The cost and timeline track compliance, the integrations you need, and whether your app is a wellness tool or a regulated medical device.

    Most healthcare apps do not fail because the idea was wrong. They fail because the team treated a medical app like a regular app, and then hit compliance, security, and integration walls halfway through the build. By then the budget is spent and the timeline is gone.

    This guide is written to keep you out of that hole. It covers what healthcare mobile app development actually involves in 2026, what it costs, how long it takes, where HIPAA and the FDA fit in, and how to choose a team that has shipped this kind of app before. We have built and shipped mobile health products since 2016, including medical translation and nutrition platforms where a wrong answer carries real consequences, so the advice here is what we would tell a founder over a call.

    Key takeaways

    • Healthcare app development means compliance and security are part of the build from day one, not add-ons.
    • Know early whether your app is a wellness product or an FDA-regulated medical device. The line is narrower than most founders expect.
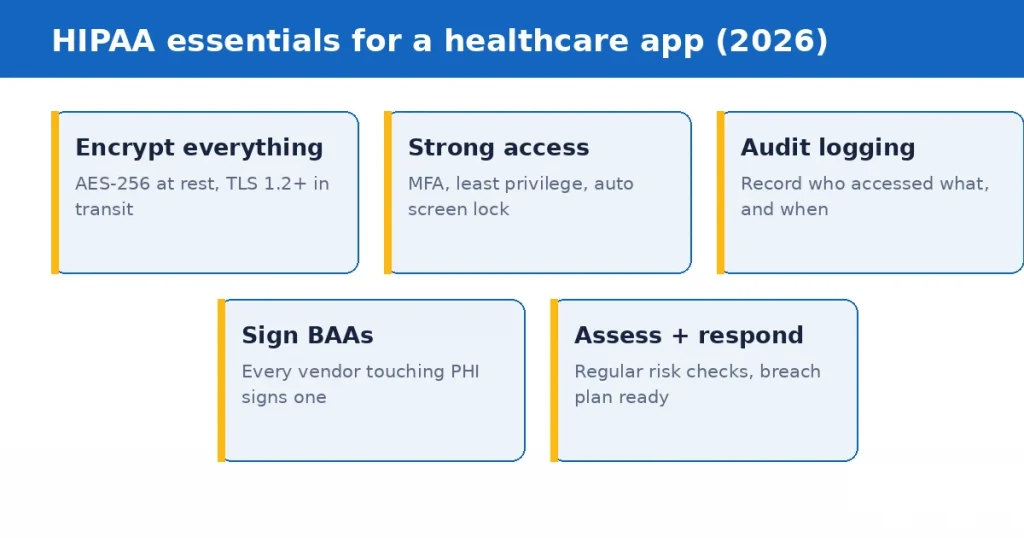
    • HIPAA in practice means AES-256 at rest, TLS 1.2 or higher in transit, MFA, audit logs, and signed BAAs with every vendor.
    • A HIPAA-ready MVP starts around $60,000 and ships in four to six months. EHR integration adds the most to both cost and timeline.
    • Choose a team with shipped healthcare apps, compliance fluency, named senior engineers, and clear code ownership.

    What healthcare mobile app development actually means

    A healthcare app is any mobile app that touches health data or clinical workflows. That covers a lot of ground: a patient booking a telehealth visit, a nurse checking a chart at the bedside, someone logging blood sugar, a therapist running a session. What ties them together is the data. The moment your app stores, moves, or displays information that can identify a person and their health, you are in regulated territory, and the rules shape every decision after that.

    This is the part founders underestimate. In a normal app, security and privacy are good practice. In a healthcare app, they are the product. Encryption, access control, audit logs, and consent are not features you add if there is time. They are the foundation the rest of the app sits on.

    Health app vs medical app: the line that changes everything

    Not every health app is a medical device, and the difference decides how heavy your build is. A wellness app that tracks steps, logs meals, or reminds you to take medication is usually a general wellness product with a lighter regulatory load. An app that diagnoses, treats, or drives a clinical decision can be a medical device that the FDA regulates as Software as a Medical Device (SaMD).

    The FDA draws the line at intended use. A blood pressure app that just displays your readings usually sits in enforcement discretion. Add a feature that interprets those readings and says you may have hypertension and should ask about medication, and you have crossed into regulated territory.

    That distinction is set out in the FDA’s guidance on device software functions and mobile medical applications. Check the current version before you finalise your feature list, because the boundary has moved more than once and it moves in the direction of more scrutiny, not less. Decide which side you are on before you build. It changes your timeline, your budget, and your legal exposure.

    HIPAA compliance: what it really requires

    If your app handles protected health information for anyone in the US, HIPAA applies. It is not a certificate you buy or a checkbox at the end. It is a set of safeguards baked into how the app is built, hosted, and run. Here is what that means in practice.

    • Encryption everywhere. Protected health information must be encrypted at rest and in transit. The working standard is AES-256 for stored data and TLS 1.2 or higher for data moving across the network.
    • Strong access control. Every user gets the minimum access they need, with multi-factor authentication, automatic screen lock, and session timeouts. On mobile specifically, that includes blocking screenshots on iOS and screen recording on Android so health data does not leak out the side door.
    • Audit logging. The system records who accessed what and when, so a breach can be investigated and access can be proven.
    • A Business Associate Agreement (BAA). Every vendor that touches the data, your cloud host, your video provider, your analytics, must sign a BAA. Using a service that will not sign one is a compliance gap by itself.
    • Risk assessments and breach response. HIPAA expects regular security risk assessments and a real plan for breach notification.
    Five HIPAA essentials for a healthcare app: encryption, access control, audit logging, business associate agreements, and risk assessment

    The Security Rule has been under active revision, and the direction of travel is toward making encryption and multi-factor authentication mandatory rather than addressable, with tighter breach timelines. Build to the stricter bar now. It is cheaper than retrofitting when a rule finalises, and none of it is wasted work even if the timeline slips.

    Founder note

    HIPAA compliance is not the whole app, it is a property of the app. It adds meaningfully to the base build cost, but retrofitting it into a non-compliant app later costs far more and sometimes means rebuilding. Start compliant.

    iOS vs Android: which platform first

    You do not have to pick one forever, but for an MVP, building one platform well beats building two platforms poorly. The right first choice depends on who your users are.

    If your users are patients in the US, iOS often makes sense first, since iPhone holds a large share of the US consumer market and Apple’s health frameworks are mature. If your app is for clinicians or serves a broad or global population, Android may matter more because of device range. If your budget is tight and you want both from day one, cross-platform is the practical answer, which brings us to the next decision.

    Native or cross-platform

    Cross-platform frameworks like Flutter and React Native let you build one codebase for both iOS and Android, which lowers cost and speeds up delivery. For most healthcare apps, that is the right call.

    You reach for native when you need heavy device-specific performance, deep integration with Apple HealthKit or Google Health Connect, or tight control over hardware like Bluetooth medical devices. Continuous glucose monitors, connected inhalers, and anything with a real-time data stream from a device tend to push you native, or at least native for that one module.

    A good team helps you decide based on your product, not on what they prefer to build. If a team recommends the same stack for every client regardless of the brief, that tells you something.

    We work across Flutter app development and React Native app development as well as native iOS and Android, and the choice genuinely changes per project.

    Core features of a healthcare app

    The exact feature set depends on whether your app is patient-facing, provider-facing, or both. These are the building blocks most healthcare apps draw from.

    • Secure sign-in and identity: MFA, biometric login, role-based access.
    • Patient profiles and health records, with consent controls.
    • Appointment booking and reminders.
    • Telehealth: encrypted video, chat, and file sharing.
    • Tracking and monitoring: medication, symptoms, vitals, often synced from wearables.
    • Notifications that respect privacy, with no health details on a lock screen.
    • EHR integration, so the app talks to the systems clinicians already use.

    The trap is trying to ship all of this at once. The apps that succeed launch with the two or three features that solve the core problem, prove people use them, and add the rest based on real feedback.

    What to cut from version one

    This is the conversation we have with almost every healthcare founder, and it saves more money than any other decision in the project.

    Cut multi-role from the first release. Building for patients and clinicians and administrators at once triples your permission model, your testing surface, and your compliance review. Pick the role that proves the product and build only for them.

    Cut EHR integration if you can prove value without it. It is the single biggest cost and schedule driver. Plenty of products validate with manual data entry or a simple export first, then integrate once a health system has actually committed.

    Cut native wearable integration. Apple HealthKit and Google Health Connect sound cheap because the SDKs are free. The cost is in the edge cases: missing data, duplicate readings, timezone drift, and users who revoke permission halfway through a study. Add it when the core loop works.

    Cut offline mode unless clinicians in the field are your users. Offline-first is a genuine engineering commitment involving conflict resolution and sync logic. It is worth it for a community health worker in a low-connectivity area. It is not worth it for an urban telehealth app.

    Do not cut audit logging, access control, or encryption. These are the things founders try to defer and they are the things you cannot add cleanly later. Every retrofit we have done started as a deferral.

    The pattern across the healthcare products we have shipped is the same: the launch feature set is smaller than the founder first imagined, and the compliance foundation is deeper. That combination ships. The reverse does not.

    EHR integration: the part that quietly drives cost

    If your app needs to read or write clinical data, it has to connect to electronic health record systems like Epic or Cerner. This is where a lot of healthcare budgets get their surprise.

    Modern EHRs expose FHIR-compliant APIs, the current healthcare data standard, which makes standard integrations relatively clean. Older systems that rely on HL7 v2 messaging or custom interface engines are a heavier lift.

    Three things drive the difference in effort:

    Which standard the system speaks. A FHIR API with good documentation is a different project from an HL7 v2 feed arriving over a legacy interface engine.

    Read or write. Reading patient data is far simpler than writing back into a clinical record. Write-back triggers a much heavier review process on the health system’s side, and their timeline is not yours to control.

    Whose sandbox you get. Some health systems have a working developer sandbox and a defined app review process. Others have a committee and a six-week wait for a call. This is often the real schedule risk and it has nothing to do with your code.

    If EHR integration is in your plan, scope it early and start the conversation with the health system before you start building. Budget and schedule both move more on this than on almost anything else.

    How much does healthcare app development cost in 2026

    There is no single price, because a wellness tracker and a telemedicine platform with EHR write-back are completely different products. The ranges below reflect what we see when scoping healthcare builds for the US market. Treat them as a starting frame, not a quote. We scope your specific app before giving a real number.

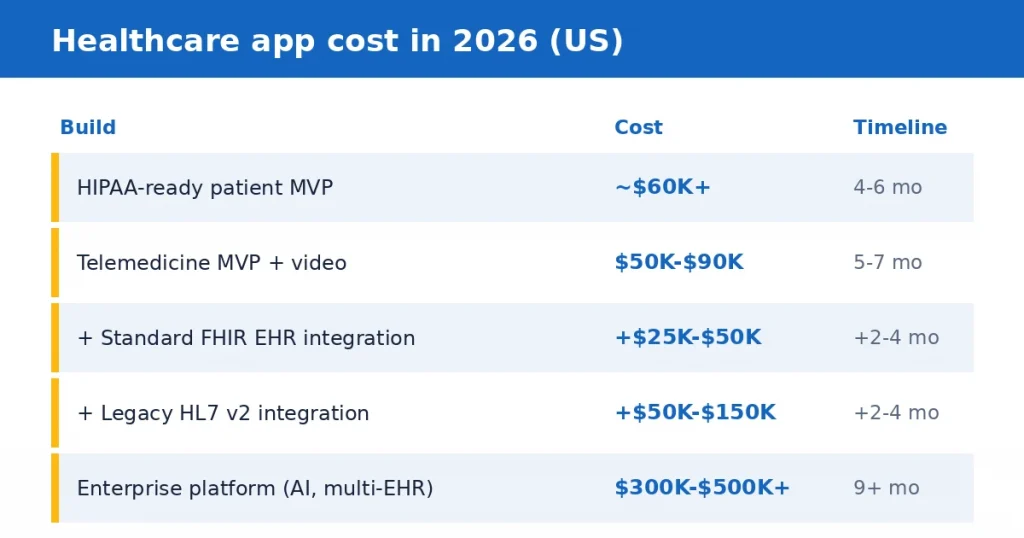
    App typeTypical cost (US, 2026)Rough timeline
    HIPAA-ready patient MVPAround $60,000 and up4 to 6 months
    Telemedicine MVP (portals, encrypted video, booking)$50,000 to $90,0005 to 7 months
    Real-time video infrastructure (add-on)$15,000 to $40,000Included above
    Standard FHIR EHR integrationAdd $25,000 to $50,000Add 2 to 4 months
    Legacy HL7 v2 integrationAdd $50,000 to $150,000Add 2 to 4 months
    Enterprise platform (AI, multi-EHR, multi-platform)$300,000 to $500,000 and up9 months and up
    Healthcare app development cost and timeline ranges in 2026, from a HIPAA-ready MVP at around 60,000 dollars to an enterprise platform above 300,000 dollars

    Compliance work is not a line item you can remove. It runs through security engineering, documentation, audit logging, vendor agreements, and testing, and it is a meaningful share of any healthcare build.

    Why healthcare apps cost more than regular apps

    The extra cost is not padding. It buys encryption and security engineering, compliance work and documentation, audit logging, signed vendor agreements, careful testing against real clinical workflows, and integrations that have to be exact because a wrong record is a patient safety issue.

    A consumer photo app can ship a bug and patch it Tuesday. A medication app cannot.

    How long does it take

    A focused HIPAA-ready MVP usually ships in about four to six months. Add telehealth video and you are closer to five to seven. Add EHR integration and you add two to four months on top.

    The timeline is driven less by screen count and more by compliance, integrations, and testing. There is also a category of delay that is not yours to control: health system review cycles, app store review for medical claims, and legal sign-off on your privacy policy and consent flows. Build slack for those into the plan rather than discovering them in month five.

    How to choose a healthcare app development company

    This is a specialist build, and general app teams get healthcare wrong in expensive ways. Here is how to tell a team that has shipped medical apps from one that will learn on your budget.

    • Shipped healthcare work. Ask for live health apps they have built, ideally in your space. Compliance experience shows up in the details they mention without being asked.
    • Compliance fluency. They should talk about HIPAA, BAAs, encryption, and the health app versus medical device line naturally, and tell you early if you are heading toward FDA territory.
    • Named senior engineers. You want senior people on your project, not a pitch team that hands the build to juniors. Ask who writes your code and whether you can interview them.
    • Clear ownership. In writing, you own the source code, the IP, and the app store listings, with no lock-in.
    • A real post-launch plan. Healthcare apps need ongoing maintenance, security patching, and OS updates. A team with no answer for month twelve is planning to disappear.

    Questions worth asking on the first call

    Five questions that separate teams quickly:

    1. Which of your healthcare apps is live right now, and can I download it?
    2. Who signs the BAA, you or the client, and which vendors in your usual stack will sign one?
    3. Based on what I have described, do you think this is a medical device? Why?
    4. What would you cut from my first version, and what would you refuse to cut?
    5. Who exactly writes the code, and can I speak to them before we sign?

    A team that has done this work answers all five without hedging. A team that has not will be vague on two or three, usually the medical device question and the one about who writes the code.

    Red flags to walk away from

    • A quote far below everyone else, which usually means compliance is missing from the scope.
    • Vague answers on HIPAA, or a promise that compliance is easy.
    • No named engineers and no shipped healthcare apps to show.
    • Fuzzy code-ownership terms.

    If you are weighing an in-house hire against an agency, our hire mobile developers page covers the engagement models, and the honest answer is that healthcare is one of the areas where prior domain experience matters more than raw headcount.

    How we approach healthcare apps at Mobilions

    We build healthcare apps compliant from the first commit, not compliant-later. That means encryption, access control, and audit logging in the foundation, signed BAAs with every vendor in the stack, and an honest early read on whether your app is a wellness product or heading toward SaMD. Senior engineers scope, build, and support the product, and you own the code, the IP, and the documentation throughout.

    We have shipped mobile health products since 2016. Careslate is a HIPAA-compliant AI medical translation app with live two-way audio built on a custom three-stage pipeline, used in clinical settings where a mistranslation has consequences. JoinBeet is a personalised medical nutrition platform with meal matching, wearable sync, and role-based admin access.

    Both are on our healthcare software development page alongside how we approach the sector, and the mobile side of that work sits under mobile app development.

    Ready to scope your healthcare app?

    Tell us what you want to build and who it is for. A senior engineer will give you an honest read on cost, timeline, and the compliance path, including the parts you can cut from the first version. Book a discovery call.

    Frequently asked questions

    How much does it cost to build a healthcare app?

    In the US in 2026, a HIPAA-ready patient MVP typically starts around $60,000, a telemedicine MVP runs $50,000 to $90,000, and enterprise platforms with AI and EHR integration reach $300,000 to $500,000 or more. The number tracks scope, integrations, and whether the app is regulated. Compliance work is a meaningful share of any healthcare build and cannot be removed from the scope.

    How long does it take to develop a healthcare app?

    A focused HIPAA-ready MVP usually ships in about four to six months. Telehealth video pushes that to five to seven months, and EHR integration adds another two to four months. Compliance and testing drive the timeline more than the number of screens, and health system review cycles can add delay you do not control.

    What is HIPAA compliance for a mobile app?

    It is a set of safeguards for protected health information: AES-256 encryption at rest, TLS 1.2 or higher in transit, multi-factor authentication, access controls, audit logging, and signed Business Associate Agreements with every vendor that touches the data. It is built into the app, not added at the end.

    Does my healthcare app need FDA approval?

    Only if it functions as a medical device, meaning it diagnoses, treats, or drives a clinical decision. Wellness trackers and appointment apps usually do not. Apps that interpret data and make clinical claims can be regulated as Software as a Medical Device. The line is narrow, so get an assessment early rather than after the build.

    What is the difference between a health app and a medical app?

    A health or wellness app tracks or supports general wellbeing, like steps, meals, or reminders, with a lighter regulatory load. A medical app diagnoses, treats, or informs a clinical decision and can be an FDA-regulated medical device. Intended use decides which one you are building, not the feature list on its own.

    Should I build for iOS or Android first?

    If your users are US patients, iOS is often a strong first choice. If you serve clinicians or a broad or global audience, Android may matter more. If you want both on a tight budget, a cross-platform build with Flutter or React Native is usually the practical answer.

    How much does HIPAA compliance add to the cost?

    It is not a separate line you can price and remove. Compliance runs through security engineering, audit logging, documentation, vendor agreements, and testing, so it raises the cost of the whole build rather than sitting beside it. Retrofitting compliance into an app built without it costs far more, so it is cheaper to start compliant.

    What is EHR integration and why does it cost so much?

    EHR integration connects your app to systems like Epic or Cerner so it can read or write clinical data. A modern FHIR integration commonly adds $25,000 to $50,000, while legacy HL7 v2 integration can add $50,000 to $150,000 and two to four months. Writing back into a clinical record is significantly harder than reading, and health system review timelines are not yours to control.

    Can I build a healthcare app without technical skills?

    Yes, most healthcare app founders are not engineers. You bring the clinical or business insight and partner with a team that handles the build and compliance. What matters is choosing a team that has shipped healthcare apps and can guide you through HIPAA and the medical device question.

    What features should my healthcare app include?

    Start with secure sign-in, patient profiles with consent, and the two or three features that solve your core problem, whether that is booking, telehealth video, or tracking. Add EHR integration, wearables, and extra features later based on real user feedback, not all at once.

    How do I make sure my healthcare app is secure?

    Encrypt data at rest and in transit, enforce MFA and least-privilege access, log every access, block screenshots and screen recording of health data, sign BAAs with all vendors, run regular security risk assessments, and test against real clinical workflows before launch.

    Does Mobilions build healthcare apps?

    Yes. We build HIPAA-compliant iOS, Android, and cross-platform healthcare apps, and have shipped mobile health products since 2016, including a medical translation app for clinical settings and a nutrition platform with wearable sync. We build compliant from day one and hand you full ownership of the code and IP.